Posts

Understanding Pedersen and Kate Commitments
Image
Cryptographic commitments play a pivotal role in ensuring the integrity and security of digital transactions and communications. Among the myriad of commitment schemes available, Pedersen and Kate commitments stand out for their unique properties and applications. This article delves into the intricacies of both, drawing insights from a previous discussion on Kate commitments Kate Polynomial Commitments . What are Pedersen Commitments? Pedersen commitments are renowned for their simplicity and elegance in cryptographic circles. At its core, a Pedersen commitment allows one to commit to a chosen value while keeping it hidden, with the ability to reveal the committed value later. The magic lies in its two-fold assurance: it's both hiding (the value cannot be guessed) and binding (the committer can't change the value once committed). The Mechanism Select Parameters : Choose a large prime number p and a generator g of a group of order q (where q is also a large prime ...

Zero-Knowledge Proofs with Circom and Noir

Image
Zero-knowledge proofs (ZKPs) are a powerful cryptographic tool that allow you to prove that something is true without revealing any additional information. ZKPs are finding a wide range of applications in blockchain, including privacy-preserving transactions, scaling solutions, and decentralized gaming. In the previous article, we've discussed about some of the fundamentals behind SNARKs and STARKs , so make sure to read those if you want more details behind the tech. ZKP Languages One of the most important components of a ZKP is the circuit. A circuit is a mathematical representation of the computation that is being performed by the ZKP. Circuits are typically written in a specialized language, such as Circom or Noir. Circom is a circuit description language that is developed by the Zcash project. It is a powerful and flexible language that allows users to write circuits for a wide range of applications. However, Circom can be difficult to learn and use, and it requires a ...

Decoding the PlayStation 3 Hack: Unraveling the ECDSA Random Generator Flaw

Image
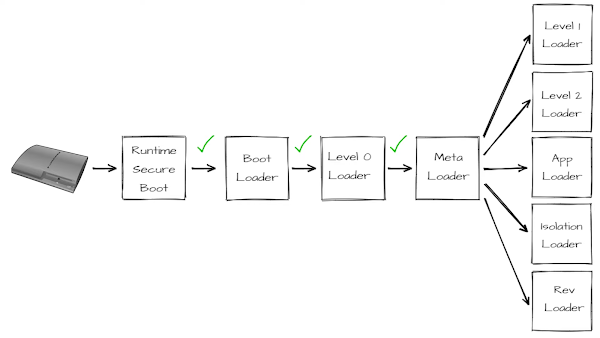
In 2006, Sony unleashed the PlayStation 3, a cutting-edge gaming console that quickly captivated the hearts of millions. However, behind its sleek design and powerful gaming capabilities lay an enticing challenge for hackers. Over the years, a myriad of attempts were made to crack the PS3's defenses, fueled by the desire to run homebrew software and pirate games. Amidst this pursuit, one group of hackers, FailOverflow, embarked on a groundbreaking mission that would send shockwaves through the cybersecurity world. In December 2010, at the Chaos Computer Congress in Germany, FailOverflow revealed a flaw that would become legendary in the annals of hacking history. Their presentation exposed a critical error in Sony's implementation of cryptographic algorithms, particularly the Elliptic Curve Digital Signature Algorithm (ECDSA) , responsible for creating signatures in the console. What they unveiled wasn't just a minor glitch—it was a seismic vulnerability. By exploiting ...

Introduction to Solana SPL Token-2022

Image
Hello fellow Solanauts! Today we're diving into the shiny new Token-2022 Solana Program Library (SPL) token standard and what it means for you as a Solana developer using the Anchor framework. Strap in, because this upgrade brings some major benefits and unlocks exciting new possibilities for Solana tokens! But first, let's make sure we're all on the same page by recapping the original SPL token program... Background: The Original SPL Token Program The original SPL token program provided a standard for creating and managing fungible and non-fungible tokens on Solana. It defined a common interface and a set of instructions for minting tokens, transferring them between accounts, setting metadata, and more. Here's a simple example of minting an SPL token using the original program: let mint = Pubkey::new_unique(); let token = Keypair::new(); let token_account = Keypair::new(); let (mint_authority, _) = Pubkey::find_program_address(&[b"mint"], &spl_to...

Proof of solvency and collateral

Image
Centralized exchanges (CEXs) are a critical part of the cryptocurrency ecosystem, but they also pose a significant risk to users. In the event of a hack or bankruptcy, users can lose all of their funds. One way to mitigate this risk is to require CEXs to provide regular proof of solvency. Proof of solvency is a way for CEXs to demonstrate that they have enough assets to cover all of their user deposits. There are a number of different ways to implement proof of solvency. One simple approach is for CEXs to simply publish a list of all of their addresses and the corresponding balances. This approach is transparent and easy to verify, but it does not provide any privacy for users. Zero-knowledge Proofs A more secure approach would be for CEXes to use zero-knowledge proofs (ZKPs) to prove their solvency. ZKPs allow exchanges to prove that they have a certain amount of assets without revealing any other information about their balance sheets. This would make it much more difficult fo...

Kate Polynomial Commitments

Image
Introduction Kate polynomial commitments are a cryptographic primitive that allow one to commit to a polynomial in a way that is both hiding and binding. This means that the commitment does not reveal any information about the polynomial, and it is impossible to change the polynomial once the commitment has been made. In simpler terms, Kate polynomial commitments allow one to lock a polynomial into a secret box. The box is locked so that no one can see what polynomial is inside, but the box is also transparent so that anyone can verify that the polynomial inside has not been changed. How Kate Polynomial Commitments Work Kate polynomial commitments are based on a mathematical object called a bilinear pairing. A bilinear pairing is a type of mathematical function that takes two elements from one group and produces an element from another group, and have many useful properties, including the ability to be used to create cryptographic commitments. To commit to a polynomial usin...

STARK vs SNARK

Image
In the world of cryptography and blockchain technology, zero-knowledge proofs have emerged as a powerful tool for ensuring privacy and security. Among the various zero-knowledge proof systems, STARK and SNARK have gained significant attention due to their unique properties and potential applications. This article aims to provide a comprehensive comparison of these two technologies, delving into their differences, advantages, and disadvantages. We will also explore the underlying mathematical concepts and commitment schemes that make these technologies possible. Understanding STARK and SNARK STARK (Scalable Transparent ARguments of Knowledge) and SNARK (Succinct Non-interactive ARguments of Knowledge) are both cryptographic proof systems that enable a prover to convince a verifier that a certain statement is true without revealing any information about the statement itself. The primary difference between the two lies in their acronyms: STARK is scalable and transparent, while SNARK ...